
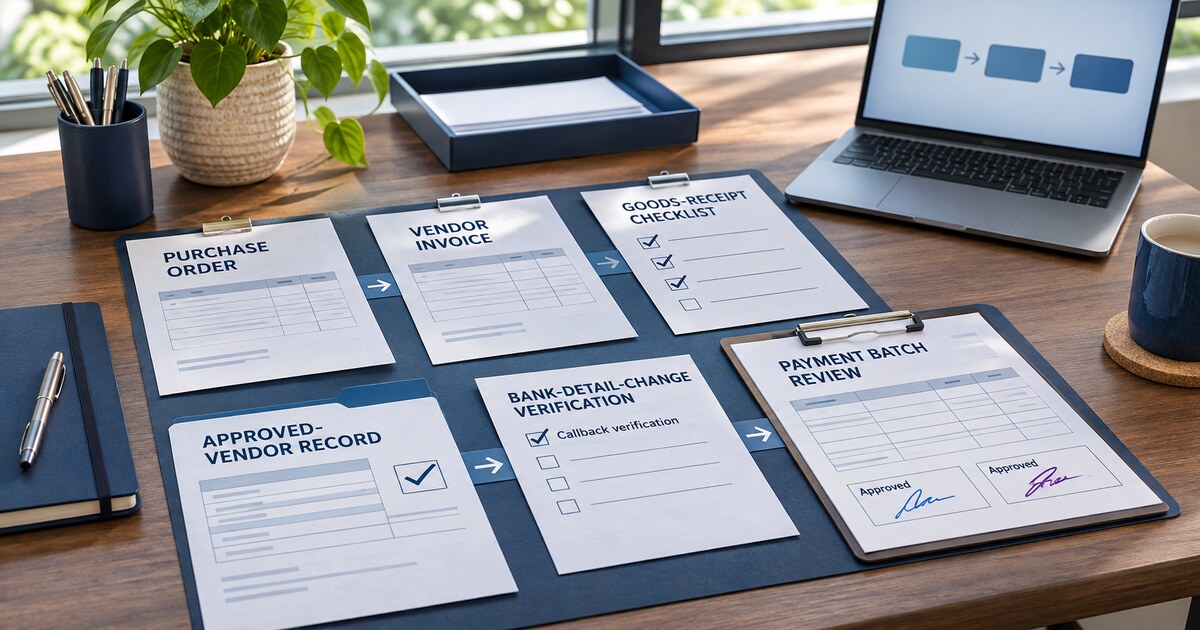
A reliable vendor payment control system separates six decisions: who may request a purchase, whether goods or services were received, whether the invoice is accurate, whether the vendor record is authentic, who may approve the payment, and who may release it. The highest-risk change—new bank details—should never be accepted from an email alone. Verify it through a second channel using contact information already on file or independently obtained, then require a second authorized person to approve the master-data change.
Small businesses do not need an enterprise procurement suite to apply these controls. They do need named roles, evidence that follows the transaction, risk-based approval thresholds, an exception log, and an independent review of bank activity. The objective is not paperwork for its own sake. It is to prevent one mistake, compromised mailbox, or dishonest insider from creating and concealing a payment.
What you need to know
- Keep vendor setup and bank-detail changes separate from invoice approval and payment release.
- Match the purchase authorization, evidence of receipt, and invoice before approving a payment whenever the transaction supports a three-way match.
- Verify bank-detail changes through a known secondary channel; do not trust the phone number or link in the change request.
- Use dual approval for new vendors, changed bank details, unusual payment methods, urgent requests, and payments above the company's risk threshold.
- Give one person no ability to create a vendor, approve its invoice, release payment, and reconcile the bank account without independent review.
- Contact the financial institution immediately if a payment may have been misdirected, preserve the evidence, secure compromised accounts, and report the incident through the appropriate channels.
What vendor payment controls must achieve
A payment process should establish that the business received a legitimate obligation, the amount and terms are correct, an authorized person approved it, the beneficiary is the intended vendor, and the payment was recorded once. It should also leave enough evidence for someone outside the transaction to reconstruct what happened. These objectives apply whether the company uses accounting software, a bank portal, spreadsheets, or a managed bookkeeping service.
The U.S. Government Accountability Office's internal-control framework distinguishes preventive controls from detective controls and emphasizes responses to fraud and improper-payment risk. For a small company, preventive controls include approved vendors, purchase authority, matching, verification, and release permissions. Detective controls include bank reconciliation, duplicate-payment review, vendor-master-change reports, and investigation of exceptions. Neither category replaces the other.
Design the controls around realistic failure modes: a fake invoice for something never ordered, a genuine invoice with changed bank details, a duplicate invoice, a payment sent before disputed work is accepted, an employee creating a false supplier, or an authorized payment altered before release. A useful control either prevents that event, detects it quickly, or limits the loss.
| Objective | Evidence | Control owner |
|---|---|---|
| Valid obligation | Approved request, contract, or purchase order | Budget owner |
| Goods or services received | Receipt, delivery record, or service acceptance | Requester or receiving owner |
| Accurate invoice | Price, quantity, tax, terms, and duplicate checks | Accounts payable |
| Authentic beneficiary | Approved vendor record and verified bank details | Vendor-master custodian |
| Authorized payment | Approval record matched to the final batch | Payment approver |
| Complete accounting | Bank reconciliation and retained audit trail | Independent reviewer |
Continue reading: GAO 2025 Green Book ↗ · Accounts Payable definition
Create a controlled vendor record before the first payment
Start with a vendor-onboarding form owned by someone other than the requester. Capture the legal name, trading name, business address, tax information when applicable, approved contact, service category, contract owner, payment terms, and conflict-of-interest disclosure. Record where each item came from. A forwarded email is weaker evidence than a signed agreement, a verified tax form, or a callback to a known company number.
For U.S. reportable payments, the IRS says the payer's first step with an independent contractor is generally to obtain a completed Form W-9 containing the correct name and taxpayer identification number. Eligible payers can use the IRS TIN Matching program before filing information returns. Treat this as a tax-data validation step, not proof that an invoice or bank account is legitimate, and restrict access to the sensitive information.
Give each vendor one durable identifier and define who may edit the master record. Require independent approval for additions, reactivations, address changes, tax changes, and banking changes. A monthly vendor-change report should show the old value, new value, editor, approver, timestamp, and supporting evidence. Disable or flag dormant and duplicate records rather than letting the vendor list grow without review.
- Reject vendor records that lack a named business owner and a documented business purpose.
- Check for duplicate names, addresses, tax identifiers, bank accounts, and near-matching spellings.
- Store tax and banking documents in a restricted location, not a shared email thread.
- Record the independently sourced contact used for future change verification.
- Review related-party or employee-linked vendors under a higher approval level.
Continue reading: IRS — Forms and associated taxes for independent contractors ↗ · IRS — Taxpayer Identification Number Matching ↗ · Finance glossary
Separate purchase, receipt, invoice, and payment
The strongest workflow prevents one person from controlling the transaction from start to finish. The requester explains the need. A budget owner authorizes the commitment. Someone with knowledge of delivery confirms receipt. Accounts payable validates the invoice. An approver accepts the payment. A different authorized user releases it. An independent reviewer reconciles the bank account. The GAO/CIGIE Financial Audit Manual identifies authorized approval, comparison with the approved vendor master, matching the purchase order, receiving report, and invoice, and independent approval of master-file changes as important control activities.
A small team may not have six different employees. Use compensating controls instead of abandoning separation. The owner can review a weekly payment packet and the bank statement while a bookkeeper prepares the batch. An outsourced accountant can perform the bank reconciliation but should not also create vendors and release payments. The essential principle is that someone independent sees the evidence before or soon after funds move.
| Decision | Primary role | Independence rule |
|---|---|---|
| Request purchase | Employee or department lead | Cannot self-approve above delegated authority |
| Authorize commitment | Budget owner | Confirms business purpose and available budget |
| Confirm receipt | Requester or receiving staff | Evidence must be independent of the vendor invoice |
| Validate invoice | Bookkeeper or accounts payable | Cannot change bank data and release the same payment |
| Approve payment | Owner or delegated manager | Reviews final payee, amount, due date, and exceptions |
| Reconcile bank | Owner or external accountant | Does not prepare and release the batch being reviewed |
Continue reading: GAO/CIGIE — Financial Audit Manual, Volume 1 ↗ · Cash flow forecast guide
Use two-way and three-way matching deliberately
A two-way match compares the invoice with the purchase order or contract. A three-way match adds evidence that the goods arrived or the service was accepted. The third document matters because a correct price does not prove delivery. For inventory, record quantities received and damaged or returned items. For services, require the responsible manager to confirm the milestone, hours, or deliverable before approval.
Define tolerances rather than letting staff decide case by case. A company might allow a documented freight difference or a small quantity variance while requiring a new approval for a price change, new fee, or changed payment term. The correct thresholds depend on the business's transaction sizes and risk tolerance; there is no universal safe dollar amount. Every override should identify the reason and approver.
Some invoices legitimately lack purchase orders, such as utilities, taxes, rent, or urgent repairs. Create a non-PO route with a named contract owner, proof of service, coding review, and approval. Do not let 'non-PO' become a shortcut for avoiding purchase authorization. Track recurring exceptions and move predictable spend into standing orders or approved contracts.
| Purchase | Expected match | Key exception |
|---|---|---|
| Physical goods | PO + receipt + invoice | Partial delivery, returns, freight, or damaged items |
| Project service | Contract/PO + milestone acceptance + invoice | Scope change or unapproved hours |
| Recurring subscription | Approved contract + active-user/owner check + invoice | Unused seats or renewal terms |
| Rent or utility | Approved agreement/account + period check + invoice | Rate change, duplicate period, or new payment instructions |
| Emergency repair | Retrospective authorization + service evidence + invoice | Urgency used to bypass vendor verification |
Continue reading: SaaS renewal calendar playbook
Lock down vendor bank-detail changes
A real vendor's compromised email account can send a convincing request to redirect a legitimate payment. The FBI describes vendor-invoice fraud as a business-email-compromise scenario, and the IC3 advises verifying changes in account information through a secondary channel. Treat every new or changed beneficiary as a high-risk event even when the message appears inside an existing email thread.
The verifier should call a number already in the approved vendor record, printed in a signed contract, or obtained independently from an authoritative source. Do not use the phone number, link, or reply address supplied in the change request. Ask a known contact to confirm the beneficiary name and the change, record the date and outcome, and have a second authorized person approve the master-data edit. For material changes, consider a risk-based waiting period or a small test payment followed by independent confirmation.
Configure alerts for vendor-master changes and the first payment to a new beneficiary. Compare the final bank beneficiary with the approved record immediately before release. A callback does not excuse weak access controls: require multifactor authentication for email and banking, remove leavers promptly, and keep audit logs for vendor edits and payment approvals.
- Pause the invoice while the change is verified; urgency is not evidence.
- Use a known secondary channel and document who was contacted.
- Require two people to approve the master-data change when staffing permits.
- Review the first payment and any returned payment independently.
- Never send complete bank details back by ordinary email as a confirmation method.
Continue reading: FBI — Business Email Compromise ↗ · IC3 — Business Email Compromise ↗
Set approval thresholds by risk as well as amount
A dollar threshold alone misses the most suspicious payments. A small first payment to a newly added bank account can test the process before a larger fraud. Build an approval matrix that considers amount, vendor status, bank changes, payment method, destination, urgency, contract status, related parties, and whether the invoice was matched. Require a higher level for any red flag even when the amount is below the normal threshold.
Write the matrix so that employees know who can approve, what evidence is required, and who acts when an approver is absent. Delegation should be time-limited and recorded. The approver must see the final payee, bank beneficiary, invoice number, amount, due date, coding, match status, and exception notes—not a vague message asking, 'Can I pay these?'.
Approve the payment batch that will actually be released. If the preparer can add a payment after approval or alter the beneficiary without invalidating approval, the control is incomplete. Bank portals should use separate maker and checker permissions, named accounts, multifactor authentication, and the narrowest access each user needs.
| Risk event | Required review | Evidence to retain |
|---|---|---|
| New vendor | Vendor setup and payment approval by separate people | Onboarding file and business owner |
| New or changed bank details | Secondary-channel verification and second approval | Callback record and change log |
| Urgent or off-cycle payment | Named senior approver | Reason urgency could not follow the normal cycle |
| Unusual payment method or destination | Enhanced verification | Commercial reason and beneficiary evidence |
| Mismatch or duplicate warning | Exception owner resolves before release | Resolution and override approval |
| Related-party vendor | Conflict-aware independent approval | Disclosure and business rationale |
Review the payment batch before release
Prepare payments on a fixed schedule when practical. A predictable cycle reduces rushed decisions and makes off-cycle requests visible. Before approval, compare the batch count and total with the supporting register, then inspect new beneficiaries, round-dollar payments, duplicates, changed due dates, credits not applied, weekend or after-hours releases, unusual currencies, and payments just below approval limits.
The checker should review a read-only batch or bank-generated approval screen and then release that exact batch. If the accounting system exports a payment file, control the folder, file creation, upload, and deletion rights. Confirm that editing a transaction after approval forces reapproval. Retain the bank confirmation and link it to the approved invoice packet.
Mark invoices as paid with the payment date and reference so they cannot be resubmitted. Keep credit notes and voids in the audit trail rather than deleting them. The Federal Trade Commission advises businesses to establish clear procedures for approving purchases and invoices and to check unfamiliar invoices rather than paying simply because the demand looks official or urgent.
- Confirm batch total, count, payment date, and funding account.
- Review every new or changed beneficiary and every unresolved match exception.
- Compare payee name and beneficiary details with the approved vendor record.
- Check invoice numbers, dates, amounts, credits, and prior-payment history for duplicates.
- Lock or reapprove any batch changed after the checker signs off.
Continue reading: FTC — Scams and Your Small Business ↗ · Revenue vs Profit comparison
Control exceptions and emergency payments
An exception process is a control, not permission to skip controls. Record who requested the exception, the reason, the missing evidence, the risk, the approving authority, and when the file will be completed. Emergency payments still require vendor and beneficiary verification. If time prevents a normal match, require a next-business-day independent review and suspend further payments until missing evidence is resolved.
Review the exception log monthly. Repeated urgent requests may reveal poor purchasing discipline, weak cash planning, a vendor manipulating deadlines, or an employee avoiding scrutiny. Group exceptions by requester, vendor, reason, approver, amount, and age. The goal is to correct the process that produces exceptions, not merely document them forever.
Do not allow seniority to erase evidence. Owners and executives are frequent impersonation targets, so a request that appears to come from the chief executive should follow the same verification rules. A short, respectful callback is cheaper than recovering a misdirected transfer.
Continue reading: Cash conversion cycle guide
Reconcile, monitor, and review access
A person who did not prepare and release the payments should reconcile the bank account promptly. Match each withdrawal to the approved payment record, investigate unknown payees and altered amounts, and confirm that rejected or returned payments were not silently redirected. Review outstanding checks or transfers, duplicate payments, unapplied credits, and manual journal entries affecting accounts payable.
Monitor the process with a small set of useful measures: vendor changes awaiting review, first payments to new beneficiaries, unmatched invoices, override count and age, duplicate warnings, returned payments, dormant vendors reactivated, and bank-reconciliation items older than the expected clearing period. These are control signals, not performance targets; a low exception count is not good if employees simply stop recording exceptions.
Review access quarterly and after every role change. Remove former employees, shared logins, unused bank entitlements, and excessive privileges. Confirm who can create vendors, edit bank details, post invoices, prepare batches, approve payments, release funds, and view tax or bank data. Test the workflow with a sample transaction and a bank-change scenario rather than relying only on a permissions list.
| Report | Question | Escalate when |
|---|---|---|
| Vendor-master changes | Were edits independently approved? | Evidence or approver is missing |
| New-beneficiary payments | Was secondary-channel verification completed? | First payment preceded verification |
| Match exceptions | Are causes resolved and recurring patterns addressed? | Old or repeated overrides accumulate |
| Bank reconciliation | Does every withdrawal map to an approved record? | Unknown, changed, or duplicated payment appears |
| Access review | Do permissions reflect current roles? | One user controls incompatible stages |
Continue reading: A–Z business knowledge index
Respond quickly to a suspected misdirected payment
If a payment may have gone to the wrong account, stop related payments and contact the financial institution immediately through a known number. Ask about a recall, hold, or fraud process and provide the transaction reference. Speed matters, but recovery is not guaranteed. Do not continue negotiating through the potentially compromised email account.
Preserve the invoice, original and changed vendor records, email headers, approval history, bank confirmation, access logs, and callback notes. Reset compromised credentials, enforce multifactor authentication, review mailbox forwarding rules, and determine whether other vendors or payments were affected. Inform the appropriate owner, insurer, legal or accounting adviser, and law enforcement or reporting service according to the organization's location and incident plan.
In the United States, the IC3 advises contacting the originating financial institution immediately to request a recall when an unauthorized transfer is discovered and reporting the incident to IC3. Businesses can also report fraud to the FTC. After containment, document which control failed—identity verification, access, approval, release, or reconciliation—and change that control before normal payment activity resumes.
- Call the bank immediately using a trusted contact route and request the available recovery action.
- Freeze related vendor changes and pending payments.
- Preserve evidence before resetting or deleting anything.
- Secure email, accounting, and bank access and review for wider compromise.
- Report through the applicable official channels and follow insurer notification requirements.
Continue reading: IC3 — Business Email Compromise ↗ · FTC — Report Fraud ↗
A 30-day rollout for a small business
In week one, map the current process from request to bank reconciliation. List every person, system, shared mailbox, vendor file, payment method, and exception. Identify incompatible permissions and select the highest-risk vendors: new vendors, vendors with recent bank changes, high-value vendors, and vendors paid through irreversible or unusual methods.
In week two, assign roles and publish the vendor-onboarding, bank-change-verification, invoice-matching, and exception procedures. Create a one-page approval matrix and a standard payment packet. In week three, configure named access, multifactor authentication, bank maker-checker permissions, alerts, and master-data reports. Train requesters and approvers using a fake bank-change scenario.
In week four, pilot one payment cycle. Sample new vendors, changed beneficiaries, matched invoices, exceptions, and the bank reconciliation. Fix gaps before expanding the process. The control set is complete only when employees can follow it under normal deadlines and the evidence is sufficient for an independent reviewer to reproduce the decision.
| Week | Deliverable | Proof of completion |
|---|---|---|
| 1 — Map | Current workflow, access map, and risk inventory | Each stage and system has an owner |
| 2 — Design | Approval matrix and four core procedures | Roles, thresholds, and exceptions are explicit |
| 3 — Configure | Named access, MFA, alerts, and maker-checker rules | A test bank-change request triggers verification |
| 4 — Pilot | Controlled payment cycle and reconciliation | Independent reviewer can trace each sampled payment |
Frequently asked questions
What is a three-way match in accounts payable?
A three-way match compares the purchase order or contract, evidence that goods or services were received, and the vendor invoice. The payment is approved when the vendor, items or scope, quantity, price, terms, and receipt agree or when a documented exception is approved.
Can one person manage accounts payable in a very small business?
One person can prepare invoices and payment batches, but an owner, manager, or external accountant should independently review high-risk vendor changes, approve the final batch, and reconcile the bank account. No preparer should be able to create a vendor, change its bank account, release payment, and conceal the result without review.
How should a business verify a vendor's new bank details?
Pause the change and contact a known vendor representative through a phone number already on file, in a signed contract, or independently obtained. Do not use the number or link in the request. Record the callback, confirm the beneficiary, require independent approval, and review the first payment.
Should every vendor payment require two approvals?
Not necessarily. The company should set thresholds based on its transaction sizes, staffing, and risk. Dual approval is especially valuable for new vendors, bank-detail changes, unusual or urgent payments, related parties, unresolved match exceptions, and amounts above a defined risk threshold.